Is a Career in Cybersecurity Right for You?
A look at what information security analysts actually do between alerts, the traits the work rewards, and the certifications that open the first door.
By Desmond Okafor-Hale · Oct 06, 2026 · 9 min read
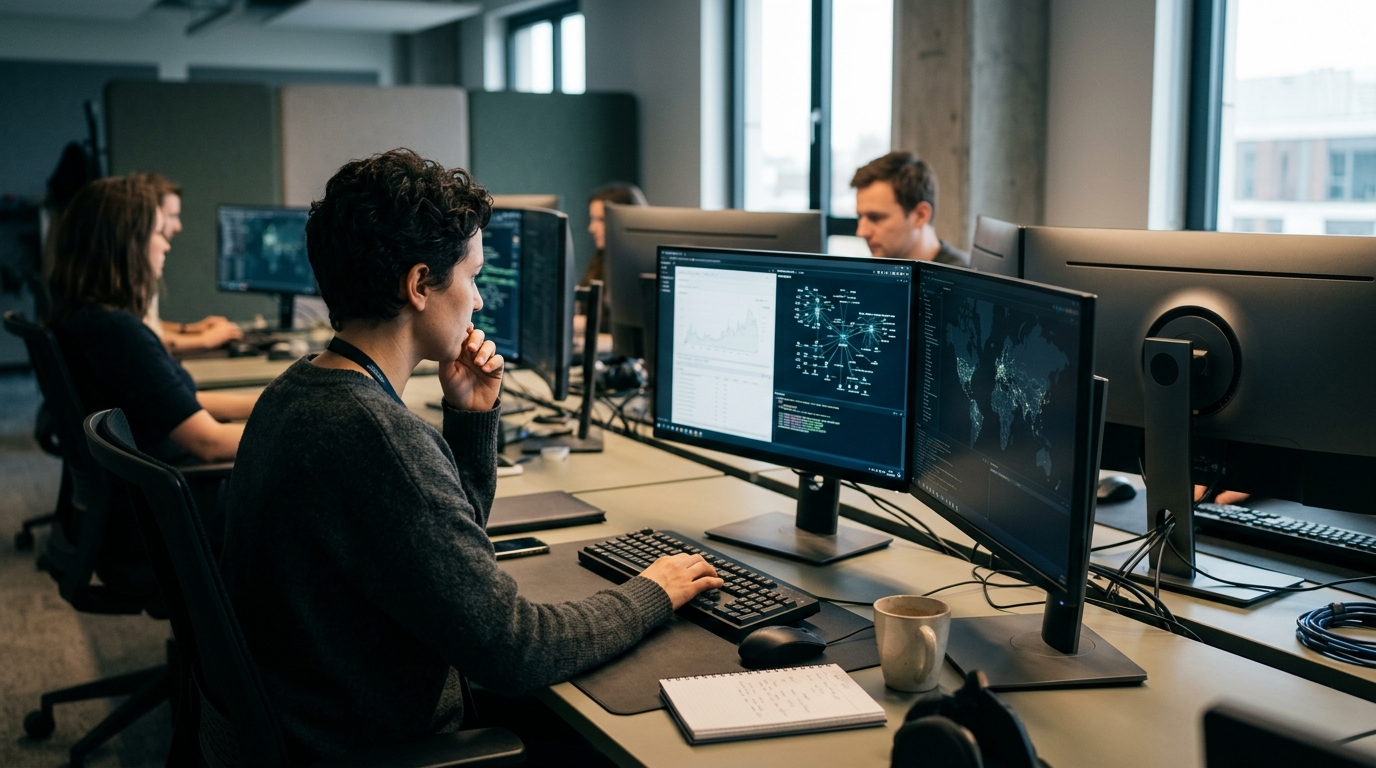
Cybersecurity work, in its most common job title, is the role of information security analyst: watching networks for breaches, keeping firewalls and data encryption software current, hunting for weak points before someone else finds them, and keeping up with how attacks are changing (U.S. Bureau of Labor Statistics, 2025). It is detailed, written-heavy, and far less dramatic than the movies suggest.
This guide walks through a realistic day, the traits that make the work feel natural rather than exhausting, where to check current pay and growth figures, and the concrete first moves if you decide it fits.
A Day in the Life
You start by clearing the overnight queue. The security information and event management console has been collecting alerts since you logged off, and most of them are noise: a sales rep logging in from a hotel network, a backup job that tripped a rule. You triage each one, mark the false positives, and write a short note on the two that need a second look.
Mid-morning is usually monitoring and maintenance. Monitoring networks for security breaches is the core duty of the job (U.S. Bureau of Labor Statistics, 2025), and that means living in dashboards. You check virus and threat reports that came in overnight and update protection systems accordingly (O*NET OnLine). You review firewall rules someone opened for a project three months ago and close the ones nobody uses any more. You confirm that data encryption software is applied to the transmissions it is supposed to cover.
Access requests arrive all day. Someone in finance needs a new application published through access management software such as Citrix cloud computing software; a contractor's account needs disabling the day their engagement ends. Administration software such as Cisco Systems CiscoWorks sits alongside that for device and configuration work, and analysts in heavier data environments also use analytical and scientific packages such as SAS or MATLAB (O*NET OnLine).
Afternoons often go to planned work rather than reactive work. You run a vulnerability scan against a segment of the network, sort the findings by what is actually exploitable rather than what scores highest, and hand a patching list to the systems administrators. Checking for vulnerabilities is a standing part of the job, as is developing plans to safeguard computer files (U.S. Bureau of Labor Statistics, 2025; O*NET OnLine).
Some part of most weeks goes to the disaster recovery plan. Analysts are heavily involved in creating it, including preventive measures such as regularly copying and transferring data to an offsite location (U.S. Bureau of Labor Statistics, 2025). That means testing whether a restore actually works, not just confirming the backup ran.
You finish by writing. A short incident summary for the one alert that turned out to be real, a plain-English note to a department head about why their request was denied, and ten minutes reading on current IT security trends, which the Bureau of Labor Statistics lists as part of the role, not an extra.
Who Thrives in This Career
- If you're good at spotting the one thing that looks slightly wrong in a long list, you'll likely enjoy the alert triage part of this job, where most of the overnight queue is noise and two items are not.
- If you're good at detail orientation, you'll likely enjoy reviewing firewall rules and access permissions, where an entry left open by accident is the whole problem. The Bureau of Labor Statistics lists detail orientation among the occupation's important qualities (2025).
- If you're good at analytical reasoning, you'll likely enjoy sorting vulnerability scan results by what is genuinely exploitable rather than working down the list in score order.
- If you're good at explaining technical decisions to people who did not ask for them, you'll likely enjoy the access-request and policy side, where you tell a department head why their shortcut is being closed. Communication skills are named as an important quality for the role (U.S. Bureau of Labor Statistics, 2025).
- If you're good at thinking creatively, you'll likely enjoy anticipating how an attacker would get around your controls, which is what creative skills mean in this occupation (U.S. Bureau of Labor Statistics, 2025).
- If you're good at structured problem-solving under time pressure, you'll likely enjoy working a live incident, where you are deciding what to isolate while the facts are still incomplete.
- If you're good at planning for things that have not happened yet, you'll likely enjoy disaster recovery work: offsite copies, restore tests, and the documentation that makes them repeatable.
- If you're good at reading steadily and keeping notes, you'll likely enjoy the research part, since tracking current IT security trends is a standing duty rather than optional background reading.
Salary, Outlook, and Requirements
| Metric | Figure | Source/Year |
|---|---|---|
| Median pay | A 2025 median annual wage for information security analysts is published in the Occupational Outlook Handbook; look up the current figure directly, as it is revised each year | U.S. Bureau of Labor Statistics, Occupational Outlook Handbook, 2025 |
| Typical entry-level education | Bachelor's degree is the typical entry-level education; the occupation is classified as Job Zone Four, "Considerable Preparation Needed," with an SVP range of 7.0 to under 8.0 | U.S. Bureau of Labor Statistics, 2025; O*NET OnLine (undated) |
| Alternative entry route | Some workers enter with a high school diploma plus relevant industry training and certifications | U.S. Bureau of Labor Statistics, 2025 |
| Work experience | Work experience in a related occupation is typically needed; many analysts arrive from a network and computer systems administrator role | U.S. Bureau of Labor Statistics, 2025 |
| Projected job growth, 2025-35 | A ten-year percentage projection and a projected employment change are published for this occupation; check the Handbook's job outlook tab for the current figures | U.S. Bureau of Labor Statistics, 2025 |
| Annual job openings | An average annual number of projected openings over the 2025-35 decade is published alongside the growth rate | U.S. Bureau of Labor Statistics, 2025 |
| Employment | A current count of information security analyst jobs is published in the Handbook's summary table | U.S. Bureau of Labor Statistics, 2025 |
| Main employers | Computer companies, consulting firms, and business and financial companies; computer systems design and related services is among the largest employing industries | U.S. Bureau of Labor Statistics, 2025 |
Pay varies by state, metropolitan area, industry, and clearance requirements. The Bureau of Labor Statistics publishes state and metro wage data separately from the national median, which is worth checking before you judge an offer.
How to Get Started
- Decide which entry route fits your situation. The typical entry-level education is a bachelor's degree, and O*NET OnLine places the occupation in Job Zone Four, "Considerable Preparation Needed." The Bureau of Labor Statistics also notes that some workers enter with a high school diploma plus relevant industry training and certifications (2025), which generally means a longer runway through hands-on IT roles.
- Build the underlying systems experience first. Work experience in a related occupation is typically needed, and many analysts enter the role after working as a network and computer systems administrator (U.S. Bureau of Labor Statistics, 2025). Help desk, desktop support, and junior systems administrator postings are the usual starting titles.
- Choose a certification deliberately. Many employers prefer candidates with information security certification; some certifications target entry-level workers and others are written for experienced practitioners (U.S. Bureau of Labor Statistics, 2025). Use the certification finder at CareerOneStop, which the Bureau names as its source for this information, to see which credentials employers list for this occupation in your state.
- Practise the duties you will be hired for. Set up a home lab where you configure firewalls, apply data encryption software, run vulnerability scans, and write the short incident notes that come out of them. These map directly to the duties listed for the occupation.
- Target the industries that actually employ analysts. Apply through the careers pages of computer systems design and consulting firms and of business and financial companies, which together account for much of the employment in this occupation (U.S. Bureau of Labor Statistics, 2025), and set alerts for the title "information security analyst" plus junior systems administrator roles at the same employers.
- Plan the step after the first job. Analysts commonly advance to lead a team, specialize in an area of information security, or move into chief security officer or computer and information systems manager roles (U.S. Bureau of Labor Statistics, 2025). Knowing which of those you want shapes whether you deepen technical certifications or broaden into management.
Frequently asked questions
Do I need to know how to code to work in cybersecurity?
Not necessarily, and it depends on the specialty. Monitoring, access control, and policy work lean on configuration and judgement more than writing software. Scripting helps you automate repetitive checks and read what an attacker left behind, so most analysts pick some up on the job. Roles touching analytical and scientific software such as SAS or MATLAB (O*NET OnLine) expect more comfort with data than with application development.
Is cybersecurity work on-call or shift-based?
It varies by employer and sector. Organisations running their own round-the-clock monitoring operate rotating shifts or an on-call rota, because alerts do not stop at six. Smaller teams usually keep business hours with an escalation phone. Consulting firms often bill project hours with occasional emergency call-outs. Ask during interviews how incidents are covered overnight and how often the rota has actually been triggered in the past year.
Can I move into security from a non-IT job?
People do, but the jump is rarely direct, because work experience in a related occupation is typically expected (U.S. Bureau of Labor Statistics, 2025). The common path runs through a support or administration role first, where you learn how networks, accounts, and backups behave normally. Auditing, compliance, and risk backgrounds transfer reasonably well into governance-side security roles, which involve more documentation and less console work.
How does this compare with general IT support work?
On matched criteria: both can be entered without a four-year degree in some cases, but security analysis typically expects a bachelor's degree and prior experience, while support roles often do not. Neither is physically demanding. The clearest difference is the work itself: support closes user tickets, while analysts spend their time on monitoring, vulnerability checks, and disaster recovery planning that nobody files a ticket for.
Does remote work exist in this field?
Often, though it depends on the employer and what you are protecting. Monitoring, scanning, and documentation travel well over a remote connection. Work involving classified systems, regulated financial environments, or physical infrastructure usually requires you on site, sometimes in a facility you cannot bring a personal device into. Consulting roles may add client travel. Check the posting's location requirements carefully, since hybrid definitions differ sharply between employers.
Sources
- U.S. Bureau of Labor Statistics — Information Security Analysts : Occupational Outlook Handbook (2025)
- O*NET OnLine — 15-1212.00 - Information Security Analysts
Written by
Desmond Okafor-Hale
Desmond writes about the mechanics of hiring: the forms, the filters, the strange rituals that decide who gets a callback. He's fascinated by the gap between what job postings say and what they mean.